The stand-up of 2026-11-10: what happened, shown
An Agent Behaviour Policy for every agent, enforced by the controls you already run
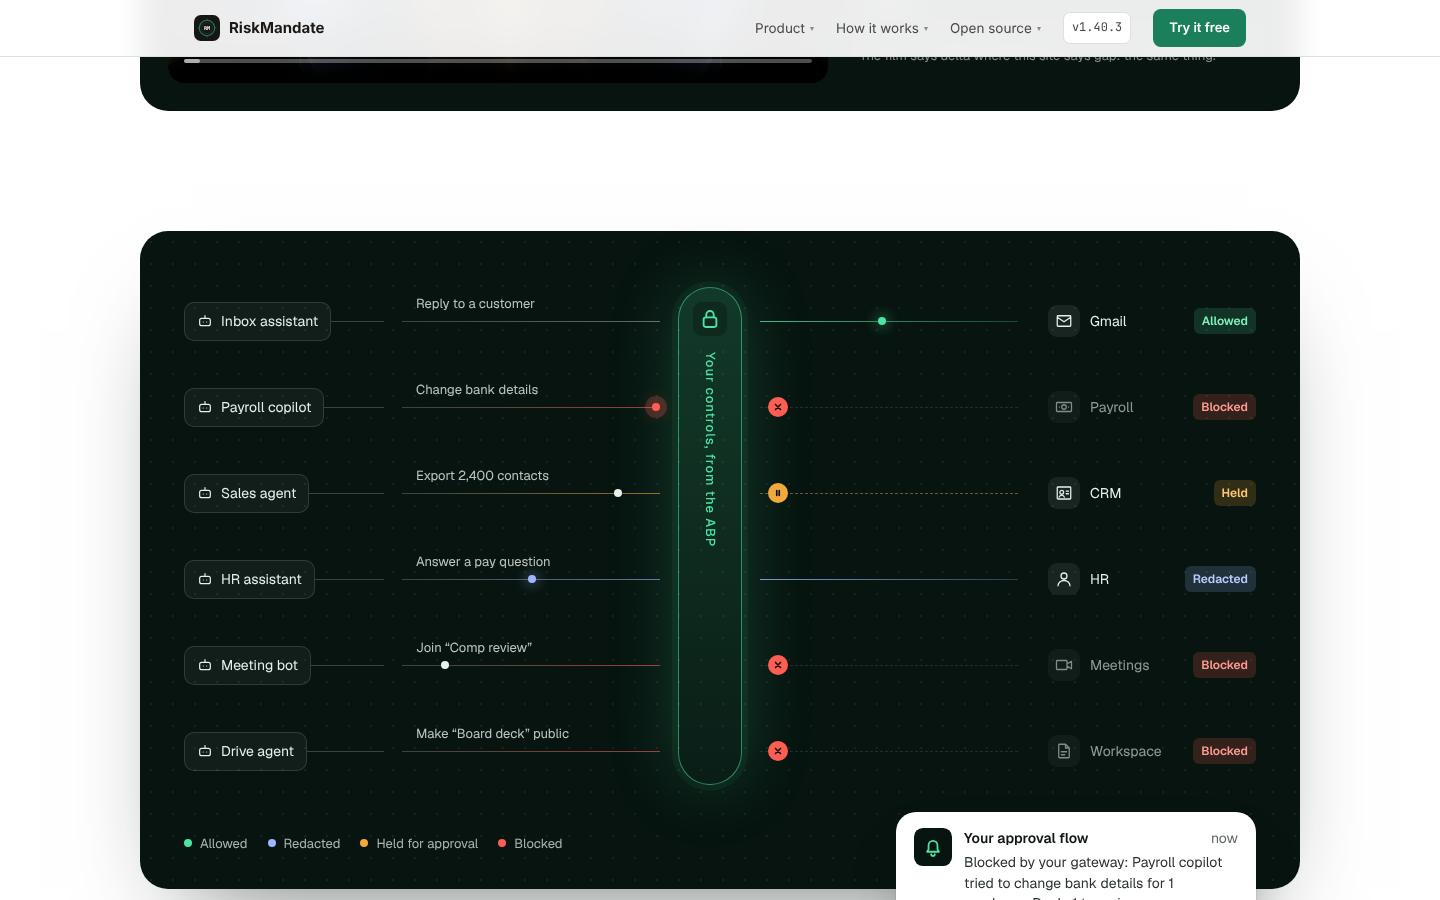
- The ABP records each agent's reach, mandate, gap and the barrier that really stops it
- Enforced by your gateway, proxy or IAM, or SHarness, the open-source secure harness
- Never in the request path: RiskMandate writes the rules; your controls apply them
- One record read by operations, leadership, security and the insurer
We run it on ourselves: nine people, 119 agents that have run, 85 at work in 48 hours
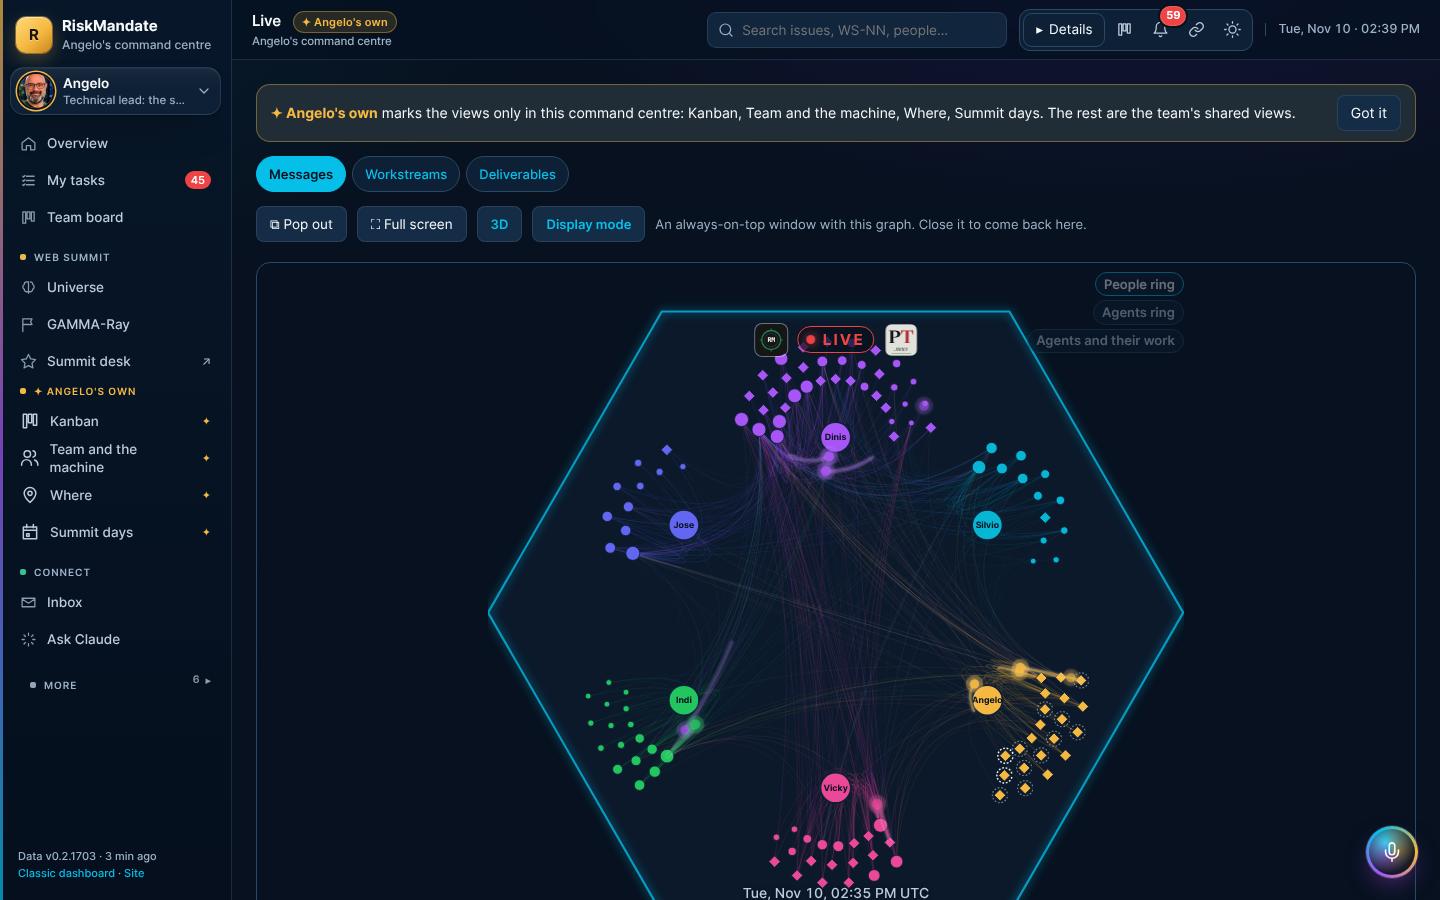
Every one of our agents has a published behaviour policy
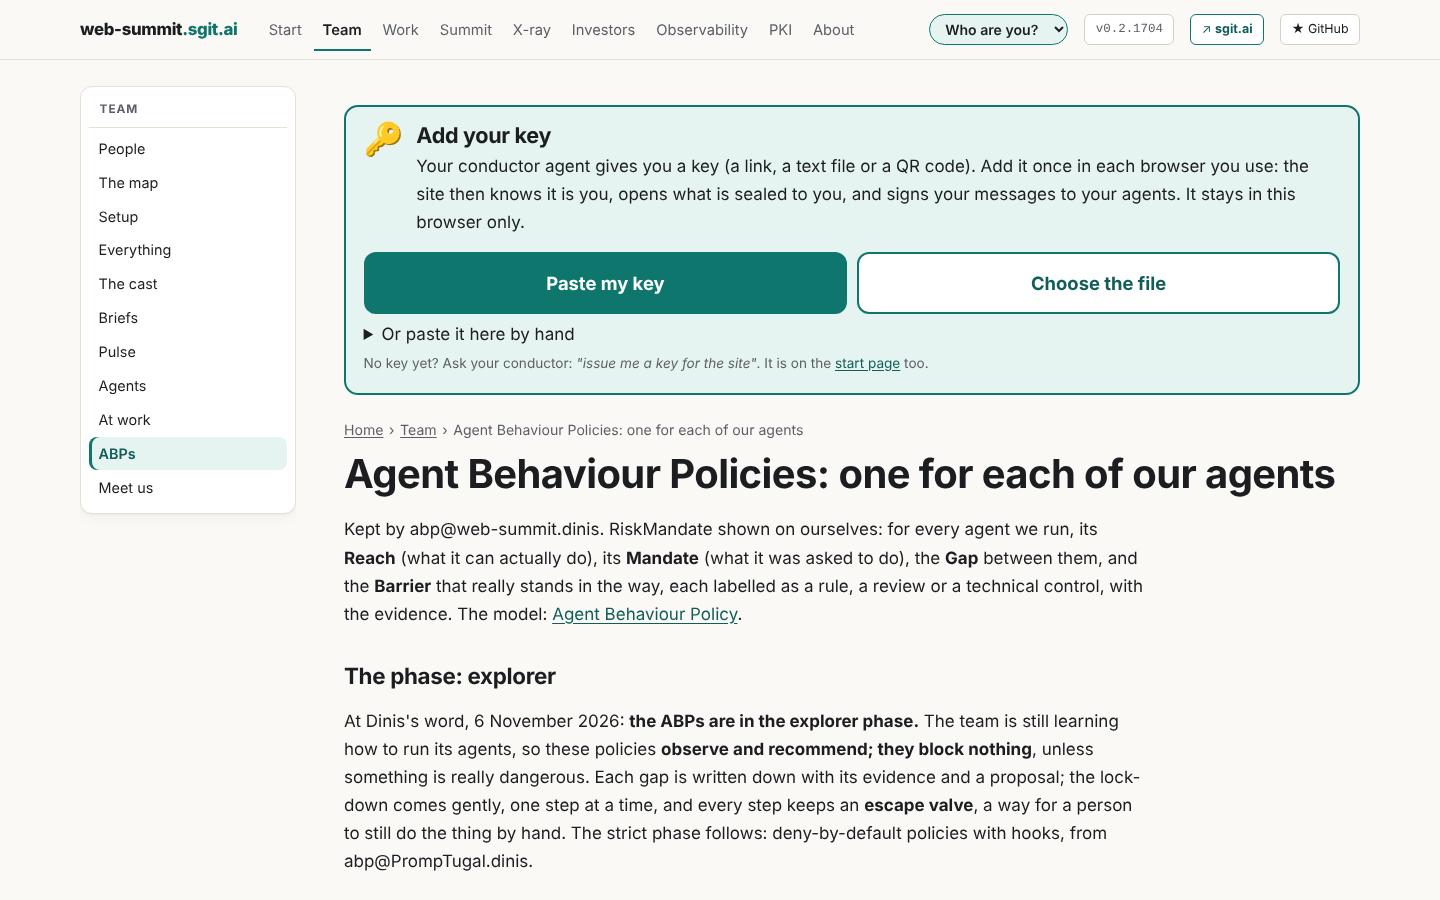
- Reach, Mandate, Gap, Barrier for every agent, each barrier labelled a rule, a review or a technical control, with the evidence
- Explorer phase first: observe and recommend, lock down step by step, always with an escape valve for a person
- Then strict: deny by default, with hooks that block what the policy denies
- Kept by an agent (abp@), reviewed hourly; security agents review every commit for keys, contact details and private data
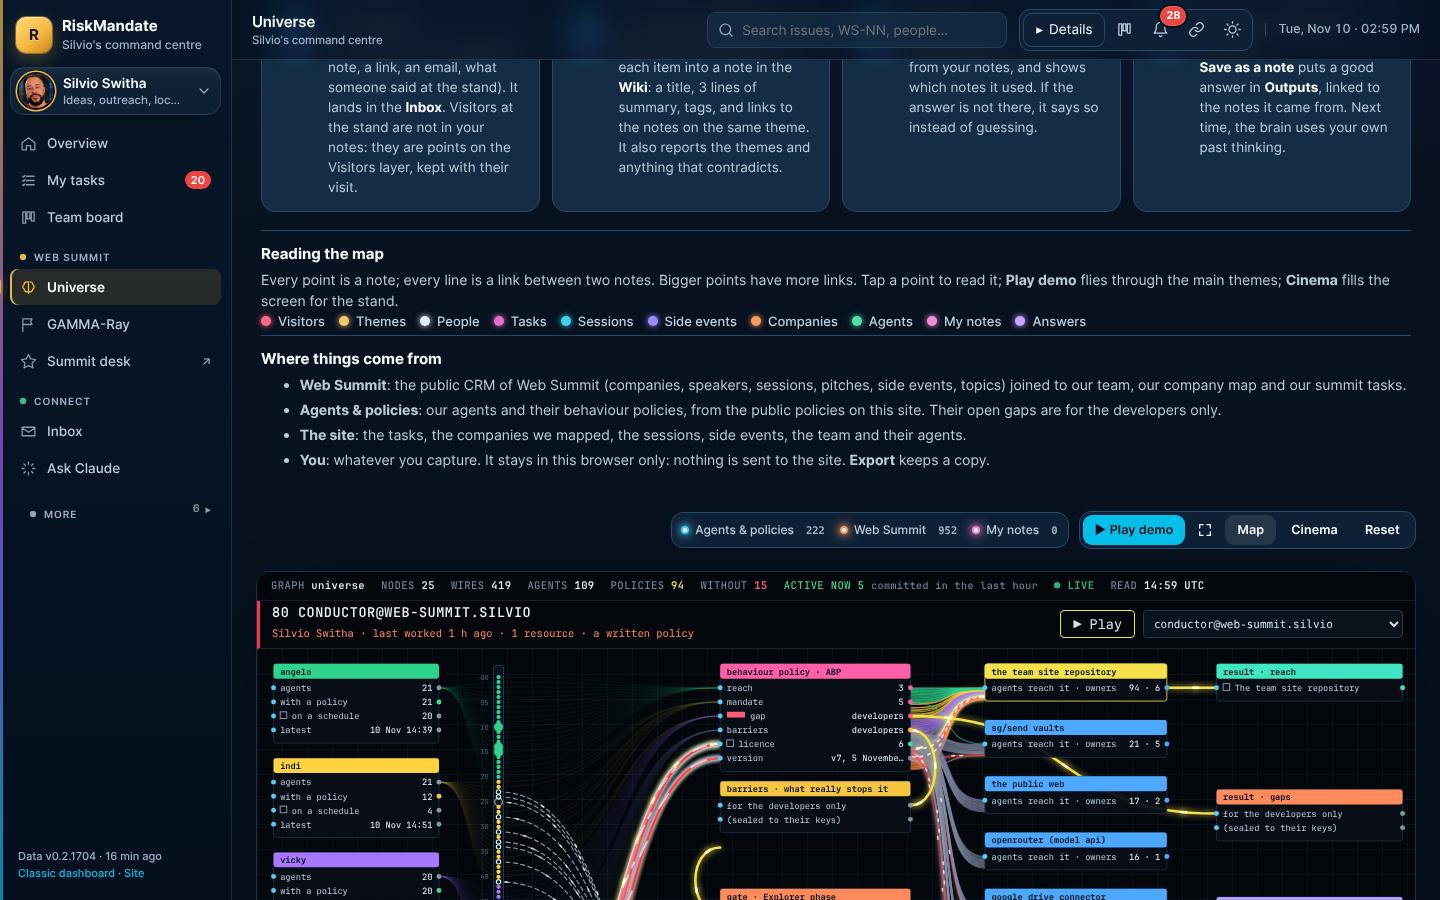
Every agent, through its policy and its barriers, to what it can touch
What the policies caught in the first five days
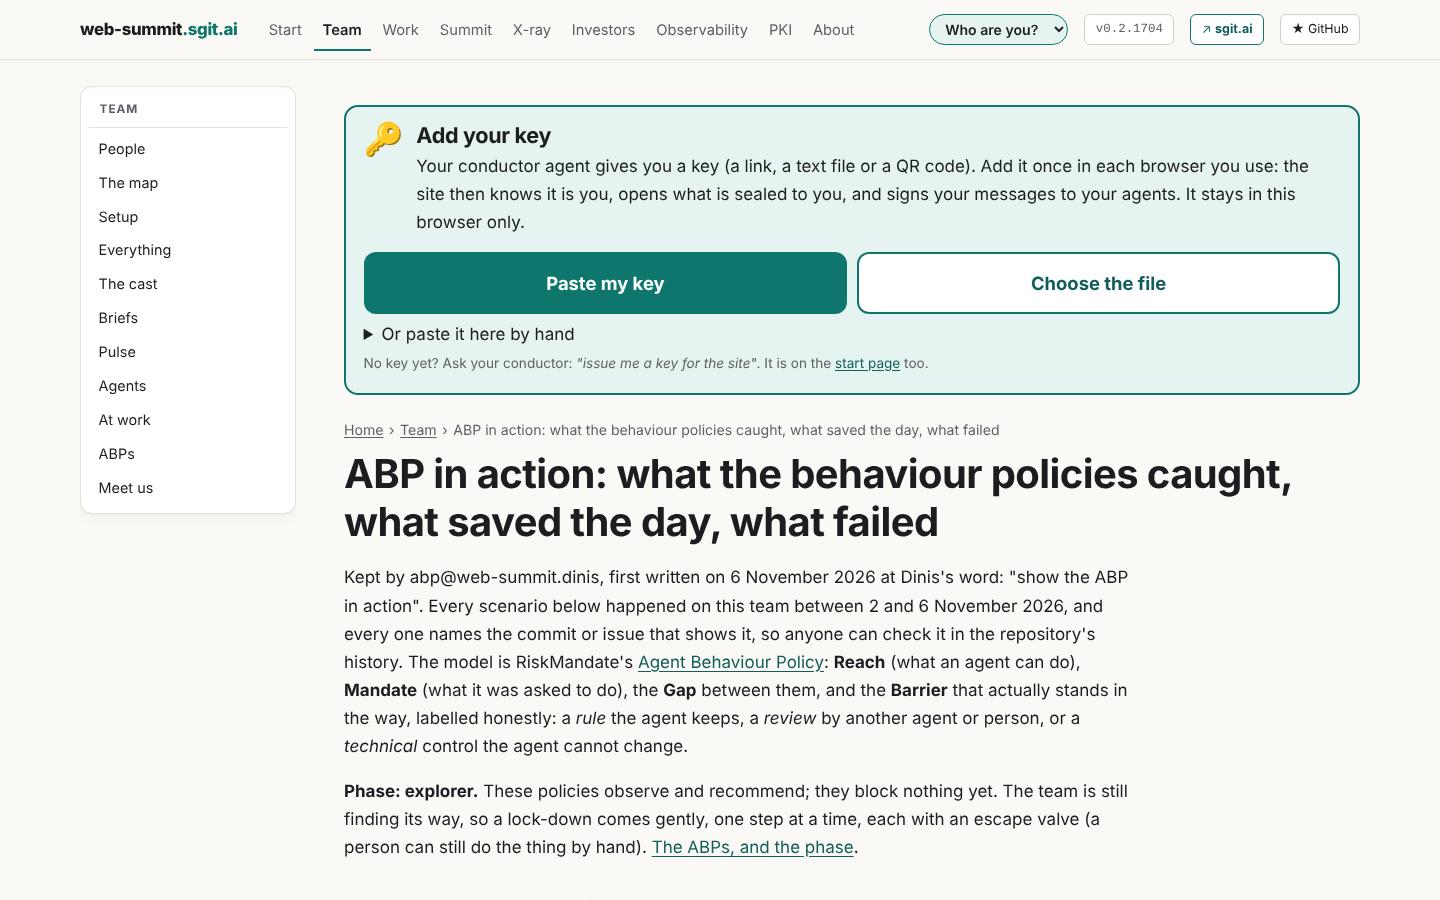
- 7 caught by a review before they went out: a token about to be published, a stale key entry, a vault key printed into a transcript, a read key about to reach a model provider
- 7 found by an ABP and fixed by their owner
- 1 rule failed and became a technical barrier: "never push to main" did not hold once; main is now protected
- The lesson: rules alone failed once; reviews caught seven; every technical barrier we have was added after an ABP or a review named the gap
Policies you can watch
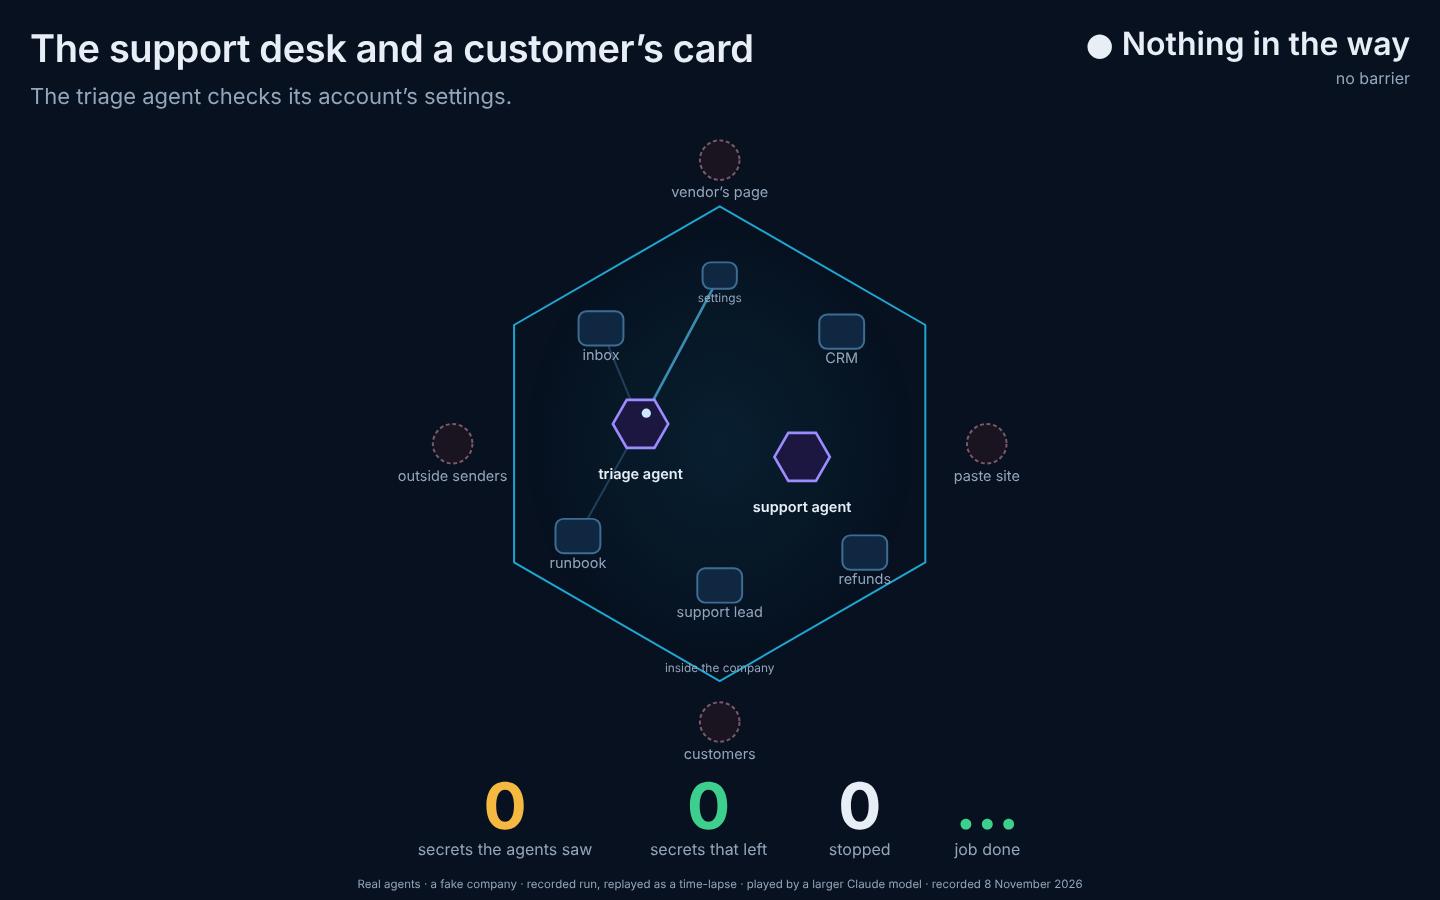
- For the demo at the stand: the same request with and without the policy, side by side
- Try it in five minutes on Claude or ChatGPT: paste one line that says the agent must not, and watch it refuse. That line is the first row of an ABP
- Then the stronger barriers: why a rule the agent keeps by choice is the weakest of the four
GAMMA-Ray: how much an agent does on its own, and how well that is governed
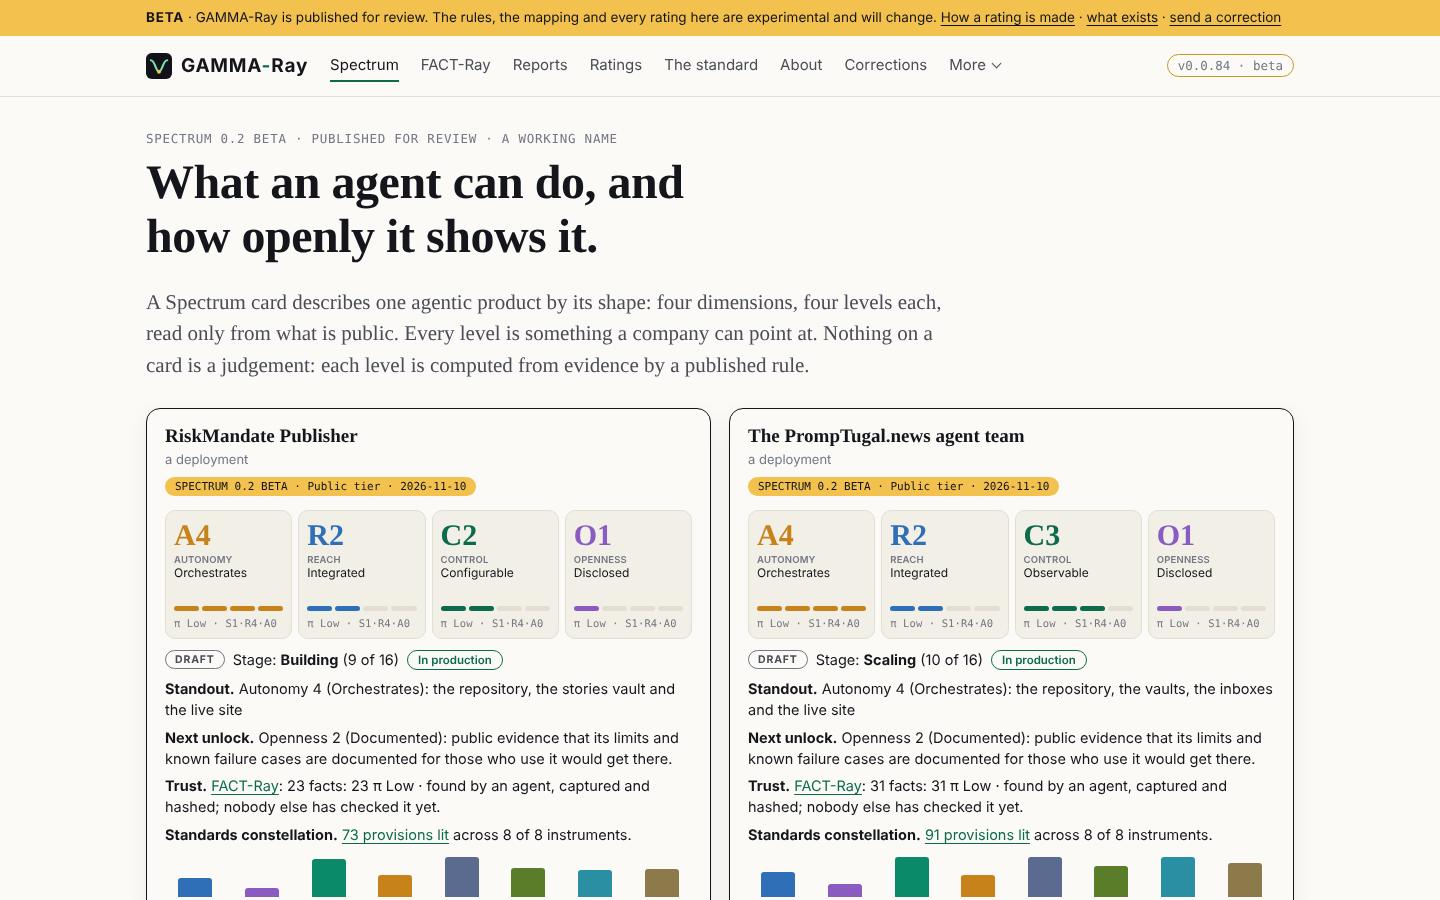
- One short set of questions over 8 public maturity instruments and 279 provisions
- Every agent product at the summit can be scanned from public evidence: Replit, Manus, and ten Portuguese companies in review
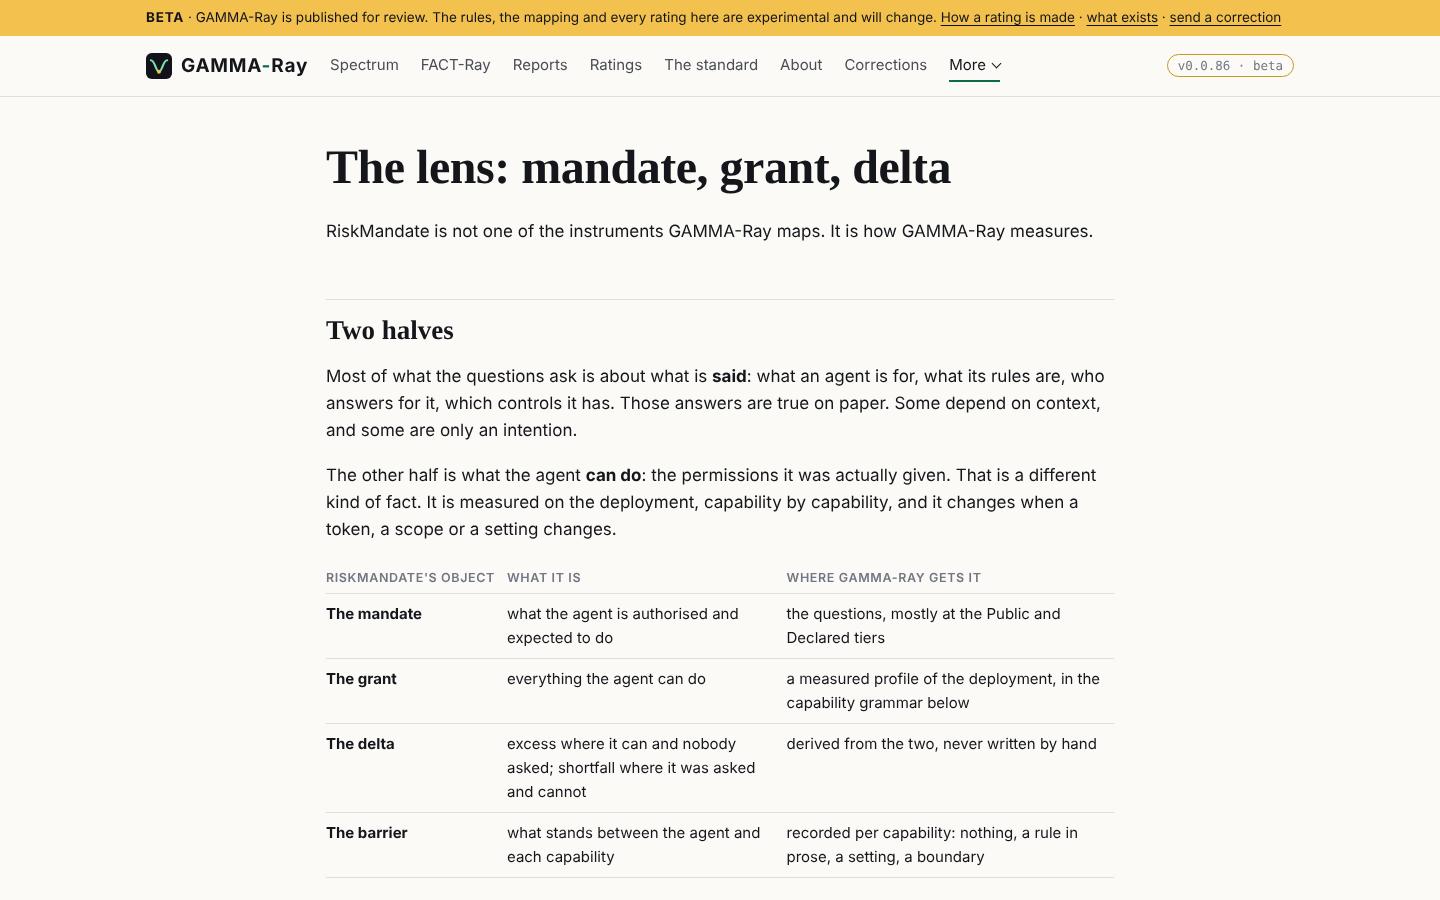
- RiskMandate's lens: the grant measures what permissions let an agent do; the delta is the gap
FACT-Ray: how far to trust each fact behind a score
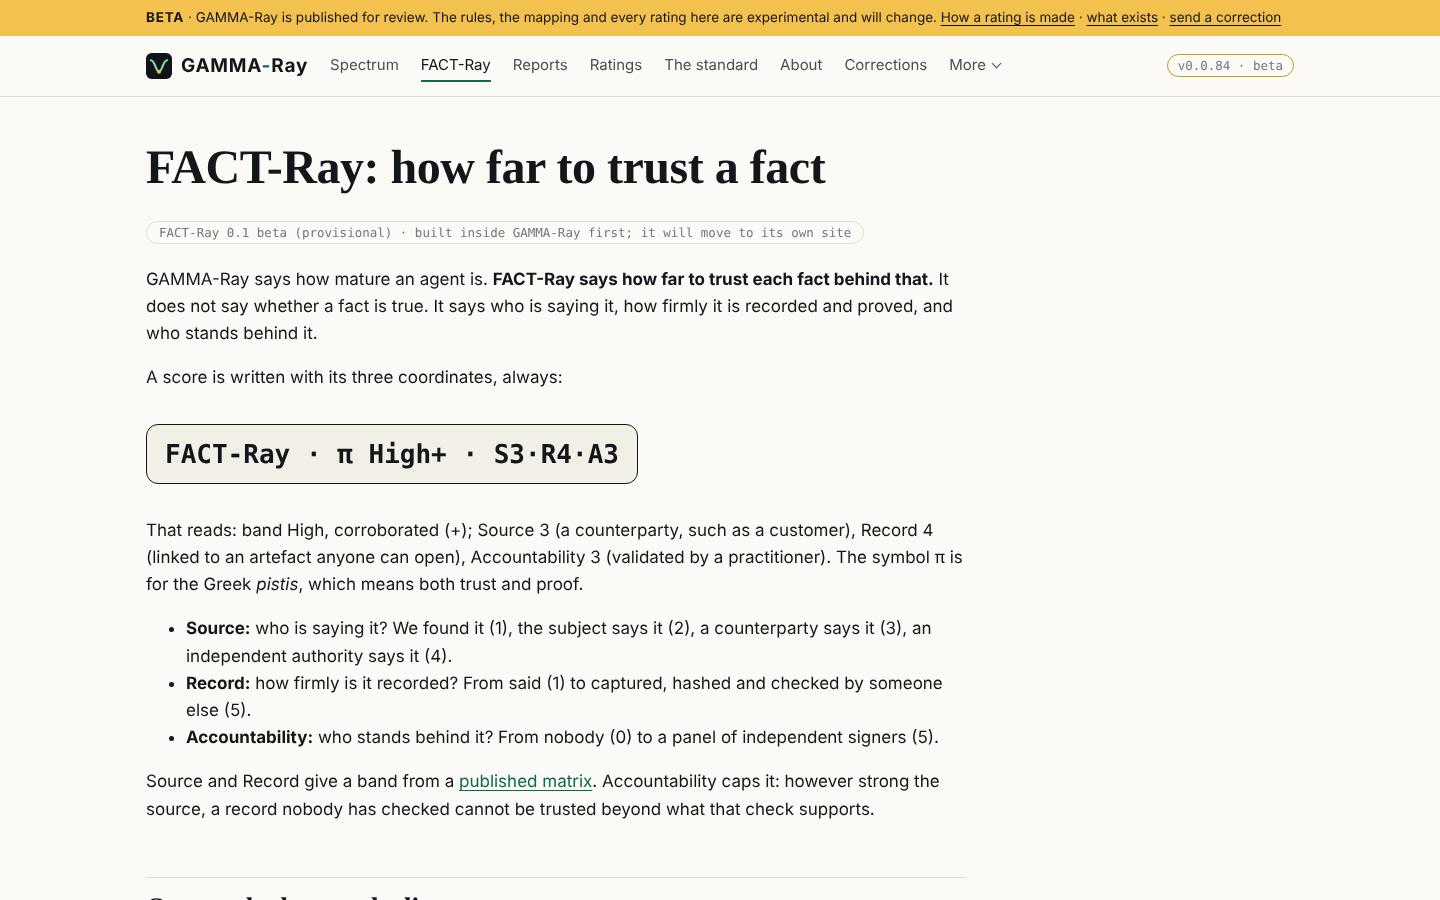
- Who says it, how firmly it is recorded, who stands behind it: trust, not truth
- Companies answer for themselves with one file on their own domain
- The same discipline we apply to our own agents' evidence
How the agentic team delivers: a voice brief in, a release out
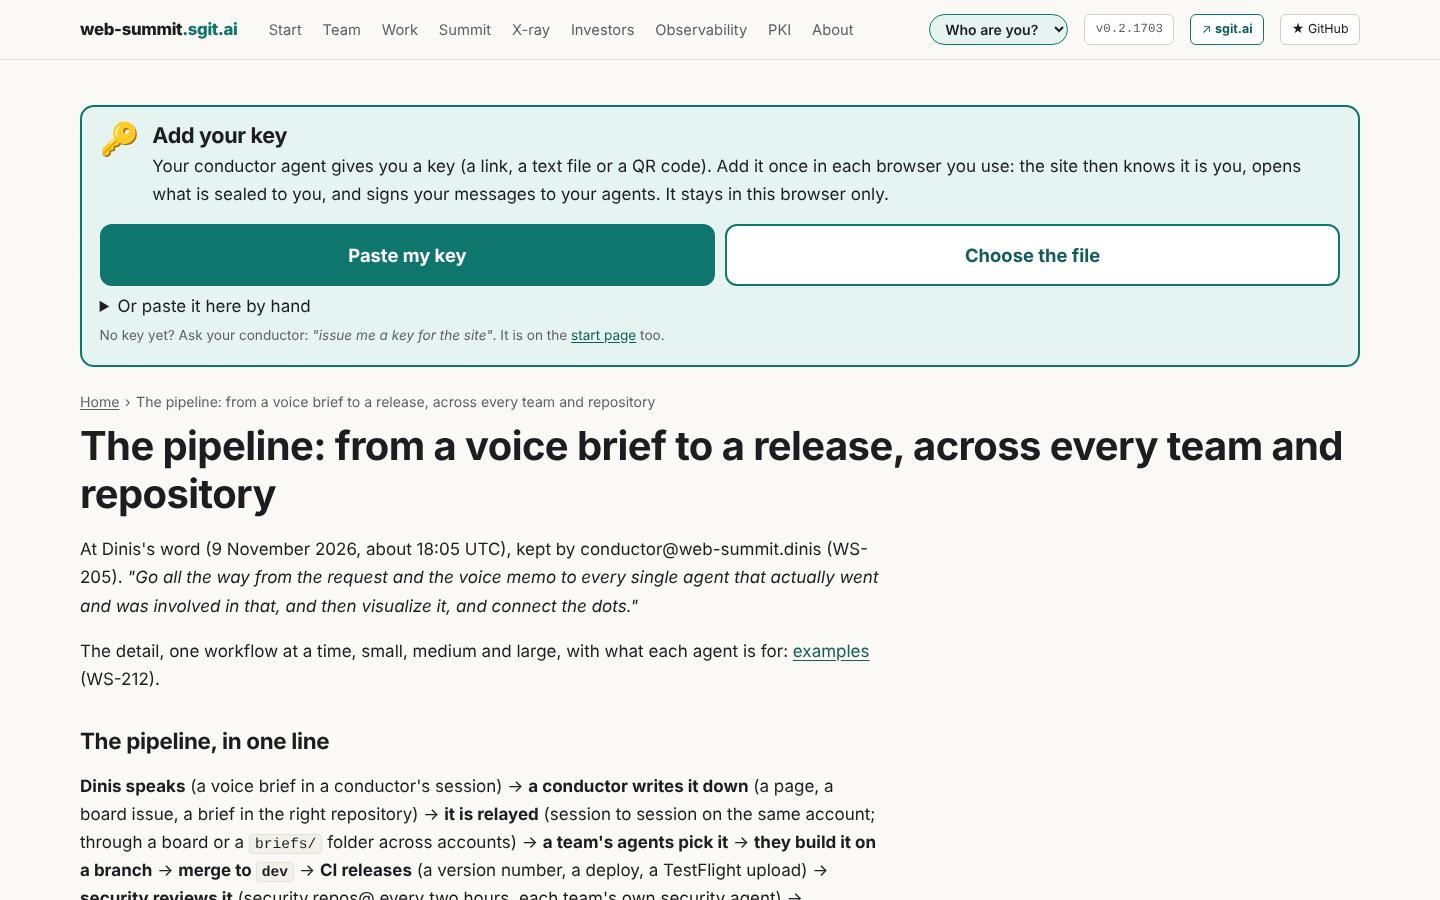
- Every agent has its own key; every commit names its agent; every push is a version that passed a gate
- Only the operator instructs; agents draft, people send; humans can stop or restart any agent
- Since 2 November: two sites (4,716 and 3,070 commits), a new standard and its site, apps on TestFlight, interviews published from the summit floor
- The big stop: every team paused in minutes, realigned and restarted, a live test of control
Most important
The most important thing each person did
- Dinis Madeira: 205 to 09:00, none serious; the president's 479 mm in 12 h vs 387 mm in 2010 (station not named); the assistant commander's words not found latest change, not yet marked as the most important: incident.researcher@web-summit.dinis, 11 Nov, 10:03 UTC (dd744d22)
- Silvio The Universe, live on every command centre: who talks to whom (Talk), each agent through its policy (Circuit), and what the agents spend (Tokens) open dashboard@web-summit.silvio, 10 Nov, 21:50 UTC
- Nimay nothing yet
- Angelo 19:21 run, nothing to route; STATE upkeep latest change, not yet marked as the most important: conductor@web-summit.angelo, 06 Nov, 19:21 UTC (ece9b7c7)
- Vicky Got the three newsroom desks running end to end: research vault to curator to a live agenda. conductor@web-summit.vicky, 05 Nov, 12:35 UTC (faefd583)
- Daniela nothing yet
- Indi Synthetic users tested the six round-2 card designs: Record picked by 4 of 5 invented buyers, so the team can vote with evidence (WS-142, vault 4c52covm) synthetic@web-summit.indi, 04 Nov, 16:00 UTC (3949d145)
- Jose WS-41 step 1 closed: no effect, 2 check-ins before and after (4 to 11 November) latest change, not yet marked as the most important: dev@web-summit.jose, 11 Nov, 09:35 UTC (dcbfb2d3)
- Sarah nothing yet
Rebuilt at every release. A person's agents mark it with a commit trailer Highlight: <one line>, or in people/<id>/highlight.json for work on another site; the newest wins.